

View: 


Categories
- Active Record
- Active Resource
- Active Support
- Administration
- Ajax
- APIs
- Authentication
- Authorization
- Background Jobs
- Caching
- Code Walkthrough
- Controllers
- Debugging
- Deployment
- eCommerce
- Forms
- Mailing
- Models
- Performance
- Plugins
- Production
- Rack
- Rails 2.0
- Rails 2.1
- Rails 2.2
- Rails 2.3
- Rails 3.0
- Rails 3.1
- Rails 3.2
- Rails 4.0
- Refactoring
- Routing
- Search
- Security
- Testing
- Tools
- Views
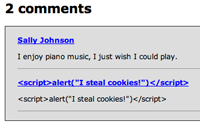
XSS Protection in Rails 3
It is easy to be vulnerable to cross site scripting attacks in earlier versions of Rails, but Rails 3 solves this by automatically escaping unsafe input.
(8 minutes)
Brakeman
The Brakeman gem will scan the Ruby code of a Rails application and alert you to common security vulnerabilities.
(8 minutes)
Hackers Love Mass Assignment (revised)
One of the most common security issues in a Rails application is the mass-assignment vulnerability which allows a user to set any attribute on the model. Learn how to prevent it in this episode.
(6 minutes)
Securing an API
There are many approaches to locking down an API. Here I start off with HTTP Basic authentication then move on to generating a unique token which can be passed through a URL parameter or HTTP header.
(7 minutes)
7 Security Tips
Security is important! Here I show seven different security flaws which are common to Rails applications ranging from mass assignment to CSRF protection.
(14 minutes)
SQL Injection
One of the most common security problems for dynamic sites is SQL Injection. Thankfully Rails does everything it can in solving this issue, but you still need to be aware of it.
(5 minutes)
Filtering Sensitive Logs
Are you accepting sensitive user data? Passwords, credit card numbers, etc. By default, Rails stores all submitted parameters in plain text in the logs. This episode will show you how to filter this sensitive input so it doesn't show up in the log file.
(2 minutes)